
In this guide
Hashing maps input data to a fixed-length digest and is designed as a one-way operation. Encryption is reversible with the correct key. The two tools solve different problems and should not be used interchangeably.
NIST describes approved hash algorithms as functions that map an arbitrary-length message to a fixed-length digest, with SHA-2 and SHA-3 families standardized for approved uses.
National Institute of Standards and TechnologyUse general hashes for integrity comparisons
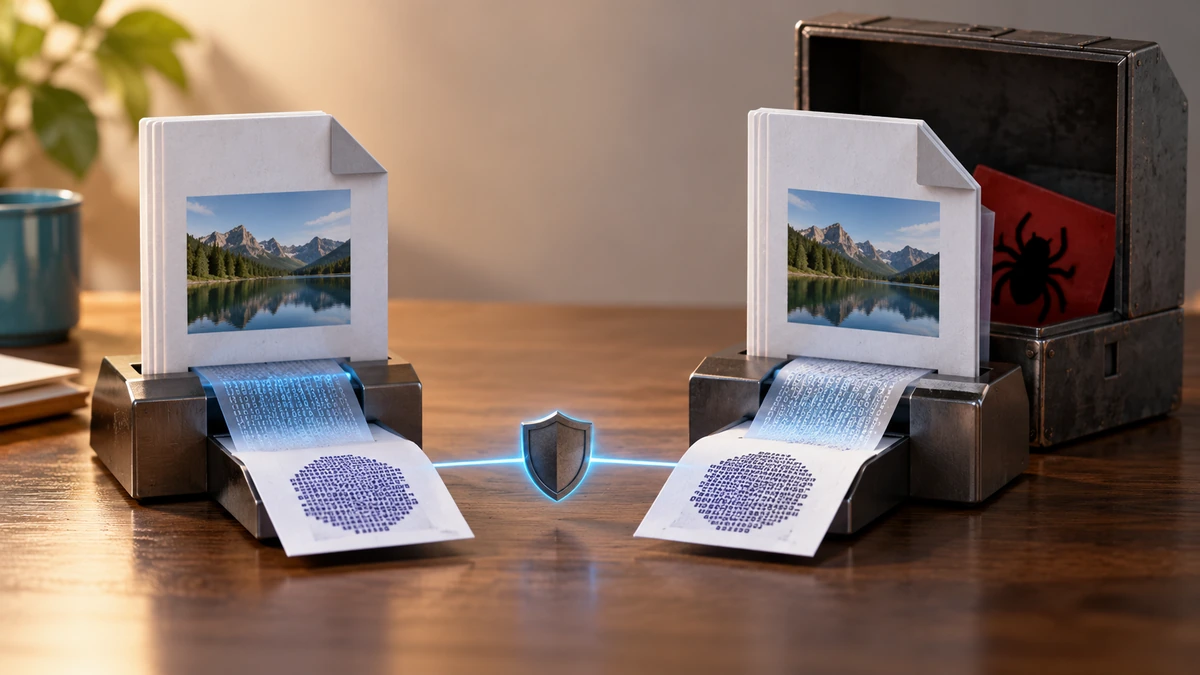
A file publisher can provide a SHA-256 digest. After download, you hash the file and compare the exact hexadecimal result. A match provides evidence that the bytes match the publisher’s referenced file, assuming you obtained the expected digest from a trustworthy channel.
MD5 and SHA-1 still appear in legacy checksum workflows, but they are not appropriate for collision-resistant security uses. NIST deprecated SHA-1 and has a transition plan away from its remaining uses; modern integrity workflows should generally prefer an approved SHA-2 or SHA-3 option.
National Institute of Standards and TechnologyPassword storage needs a deliberately slow function
Fast hashes such as SHA-256 are designed to process data quickly, which also helps attackers test many password guesses quickly. OWASP recommends password-specific, adaptive algorithms such as Argon2id and treats bcrypt mainly as a legacy choice where Argon2 or scrypt is unavailable.
OWASP FoundationPassword storage also needs a unique salt for each password and a cost setting tuned to the system. A plain hash-generator output is not a complete password-storage design.
- File checksum: use a modern general-purpose hash such as SHA-256 when the publisher specifies it.
- Password storage: use a password-hashing library and current parameters.
- Confidentiality: use appropriate encryption, not hashing.
A matching hash proves limited things
A matching digest shows that two byte sequences produced the same digest under the chosen algorithm; with a modern collision-resistant hash, that is useful integrity evidence. It does not prove the file is safe, authentic, or free of malicious content unless the expected digest itself came from an authenticated source.
Use a hash generator for learning and checksums. Do not paste real passwords, private keys, or confidential data into tools you do not trust.
Key takeaways
- Hashing and encryption serve different goals.
- Use SHA-2 or SHA-3 for modern integrity workflows when specified.
- Use Argon2id, scrypt, bcrypt, or PBKDF2 through a proper password library—not a plain fast hash—for password storage.
Sources
References for factual claims and further reading.
- 01
National Institute of Standards and Technology
Hash Functions - 02
OWASP Foundation
Password Storage Cheat Sheet
Educational information only. Follow the requirements of the receiving organization, product label, applicable standard, or qualified professional for your situation.